
The Kempinski hotel group has confirmed that a login credential belonging to one of its technology partners was misused to access guests’ booking data, which was then used to request payments from them by posing as its hotels. In a notice published on its website and dated 12 November 2026, the group states that no payment card data is involved, but that it cannot rule out passport or visa numbers having been affected.
- 🔑 What happened · a login credential belonging to a third-party technology partner was used by an unauthorised person.
- 📋 Data exposed · names, stay dates, hotel name, itinerary numbers, mobile numbers and email addresses.
- 💳 Payment cards · not affected: according to Kempinski, they are not stored in the compromised system.
- 🛂 Passport or visa · the group can neither confirm nor rule out that these numbers were affected.
- ☎️ What to do · contact the hotel directly using the details published on Kempinski’s official website.
A partner’s login credential misused
Kempinski’s statement runs to just a few paragraphs, published in English under the title “Reservation Security Notice”. In it, the group confirms a security incident involving guests’ booking information: a login credential used by one of its third-party technology partners was misused by an unauthorised person, who was able to view that information.
The data was then used to contact guests by posing as the group’s hotels, in order to request payments from them. The notice does not specify the channel used for these messages, the partner’s name or the number of people contacted.
Access revoked, investigation led by an expert
As soon as it became aware of the incident, Kempinski says, the group revoked the credential and closed the access route, then launched an investigation with the support of an independent cybersecurity specialist. The unauthorised access has now been blocked, and Kempinski says it is working with the partner concerned to better protect the data they share.
The group has also notified the relevant data protection authorities, as it is required to do, without saying which ones. It offers its apologies in these words: “We sincerely apologize for causing concern and are doing everything we can to support impacted guests”.
Names, stays, emails: the data exposed
According to the investigation, the exposed data is limited to three categories of information: guests’ names, their booking details (stay dates, hotel name and itinerary numbers, in other words booking references) and their contact details, namely mobile phone numbers and email addresses.
On the payment side, Kempinski states that no payment card data is involved: cards are not stored in the affected system and were not accessed.
Passport or visa: the question remains open
On one point, the notice remains cautious. Kempinski writes that it can neither confirm nor rule out that sensitive personal information, such as passport or visa numbers, was affected. The group does not say which bookings contained such details or how it intends to settle the question.

Asked to pay? Contact the hotel directly
For any questions, Kempinski asks guests to contact the hotel concerned directly, using the details published on its official website; a page on kempinski.com lists the contact details for each property.
For security questions, or to check whether a message received is genuine, the group provides a contact form at the bottom of its notice to guests. These are the only instructions Kempinski has given so far.
What Kempinski has not yet said
Several questions remain without an official answer: the number of guests affected, the list of hotels concerned, the period covered by the exposed bookings, the date on which the access was discovered and the name of the technology partner. For now, the notice is only available in English.
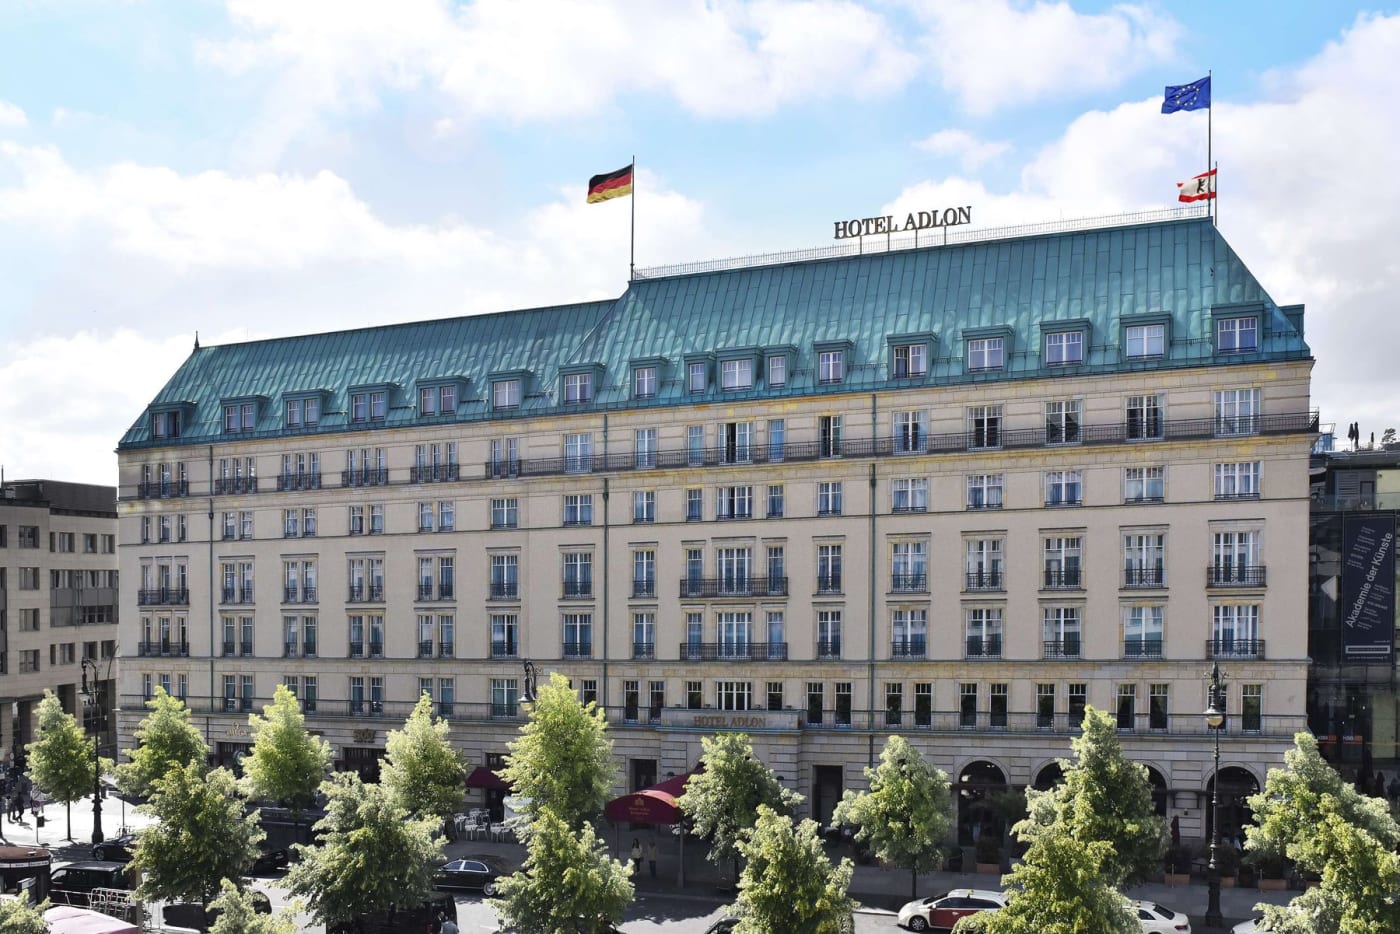
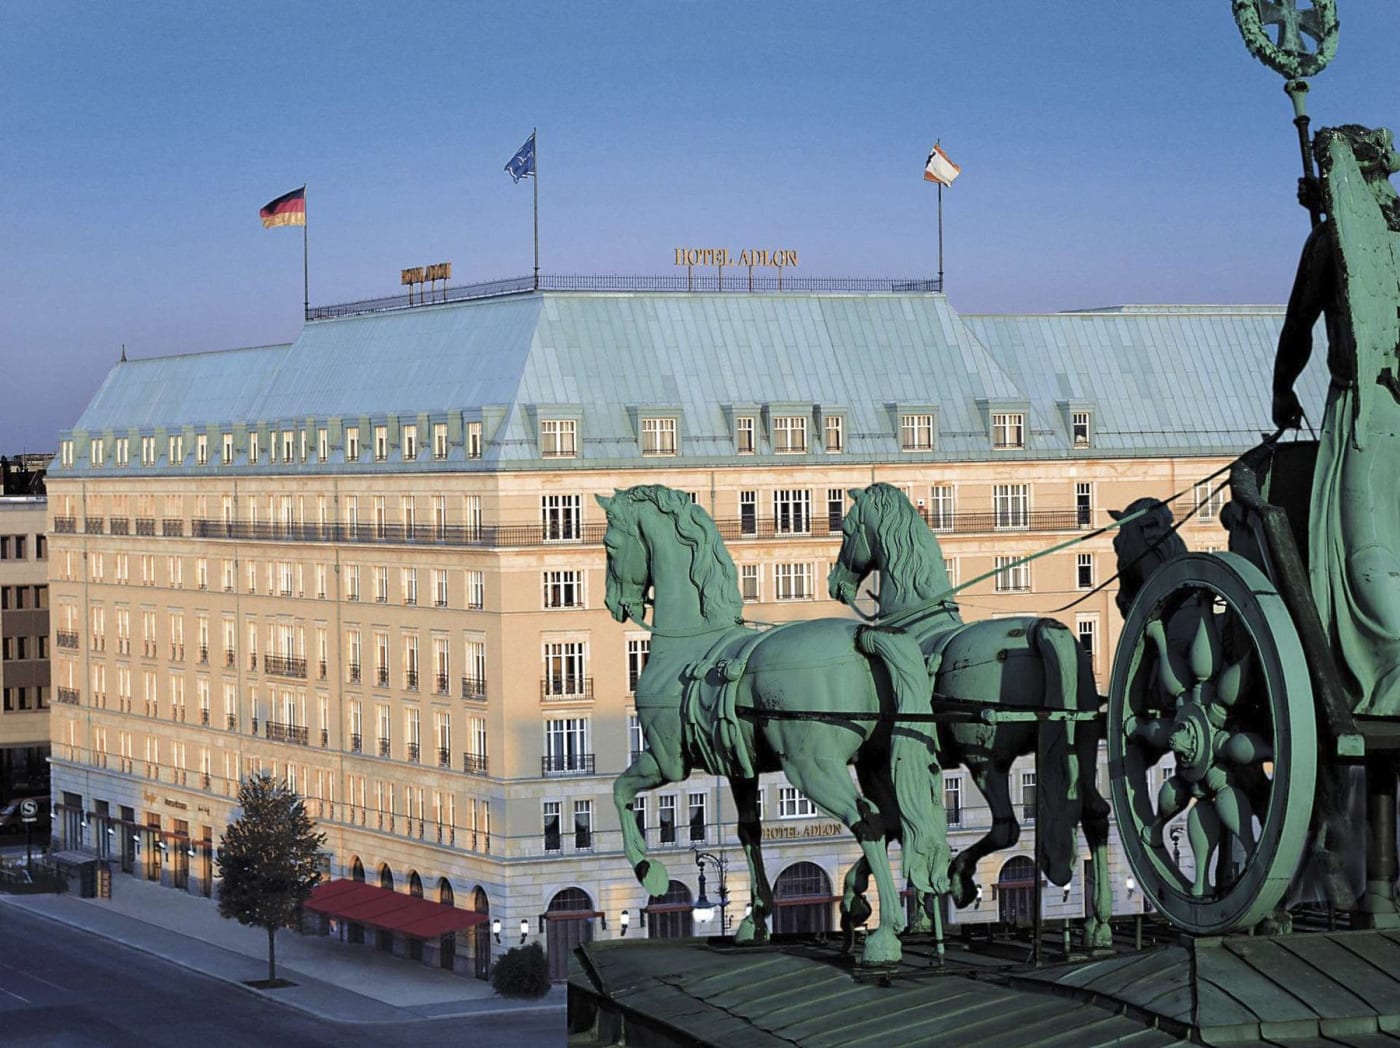
Founded in 1897, Kempinski describes itself as the oldest luxury hotel company in the world. Its addresses include the Hotel Adlon Kempinski in Berlin and the Kempinski in Cancún, Mexico, and it has acquired the Augustine in Prague, which it will relaunch in early 2027.
- 🏢 Group · Kempinski AG, Maximilianstraße 17, Munich (Germany), according to the legal notice on kempinski.com
- 📅 Official notice · Reservation Security Notice, updated 12 November 2026, in English
- 📋 Data exposed · names, stay dates, hotel name, itinerary numbers, mobile numbers, email addresses
- 💳 Not affected · payment card data, which is not stored in the compromised system
- ❓ Unresolved · passport or visa numbers, neither confirmed nor ruled out
- ☎️ Hotel contacts · kempinski.com/en/hotel-contacts